An engineer’s last day is Friday. Their laptop is returned, the staffing partner confirms the assignment has ended, and IT disables the main account. On Monday, a release fails because a publishing job depended on that engineer’s personal token. Meanwhile, a repository deploy key still works.
An IT offboarding checklist for an engineering team has to prevent both failures. It must close the departing person’s access and preserve the organization’s ability to build, deploy, diagnose, and recover its software. Those are separate outcomes, and neither should be inferred from an HR ticket marked complete.
This is a practical operating framework for CTOs, engineering managers, and IT or security leads overseeing employees and embedded contractors. It is especially relevant to nearshore staff augmentation, where the client manages daily work and its own systems while the provider coordinates the professional’s assignment. It complements—not replaces—your organization’s approved HR, security, records-retention, and incident-response procedures.
What your IT offboarding checklist must prove
Use seven controls to turn an exit into a coordinated change: assign accountability, inventory access, revoke human access, separate automation from personal credentials, demonstrate the handover, verify closure, and agree provider responsibilities before the next engagement.
The underlying distinction is not new. NIST’s personnel security controls address both revoking a departing person’s credentials and retaining organizational access to information they previously controlled. They also address notification responsibilities for external providers. Treat that as a useful control model, not a claim that following this article establishes compliance.
For every important system, your final record should answer two questions: who can still access it, and who can now operate it? A signature without supporting evidence answers neither.
1. Name one exit owner and an exact cutoff
Assign one client-side owner to coordinate the exit. That person does not need administrator rights everywhere. They need authority to gather the relevant owners, track unresolved tasks, and escalate decisions. In a small team, this may be the engineering manager; in a larger organization, an established IT or security workflow may provide the coordinator.
Record the last authorized working time with a date, time, and time zone. Distinguish the contract end date from the system-access cutoff if they differ. Confirm who authorizes changes and how the team will handle a late schedule change. “End of day” is not precise enough for distributed teams.
Divide responsibilities explicitly:
- Client manager: confirms business ownership, work reassignment, and which delivery activities must continue.
- IT and security owners: execute identity, device, session, and system-access controls under approved procedures.
- Technical successor: demonstrates that the remaining team can use the required repositories, pipelines, environments, and runbooks.
- Staffing provider: coordinates assignment changes, availability for agreed handover work, provider-managed equipment or accounts, and completion evidence within its control.
For a planned departure, use the notice period for authorized transfer and rehearsal. For an immediate exit or suspected compromise, security containment takes priority; do not extend access merely to finish documentation. The remaining team must reconstruct missing knowledge using authorized records and systems.
Put both paths in the IT offboarding checklist. A plan that assumes a cooperative two-week handover is incomplete, but treating every routine departure as an incident is unnecessary. HR and security should determine the applicable path and communications, not a generic template.
2. Inventory access, ownership, and dependencies separately
Start with the identity provider, but do not stop there. Compare its application list with repository membership, cloud accounts, secrets-management records, device inventory, procurement records, and the engineer’s current responsibilities. Include non-SSO applications and direct customer access. Use a manager-reviewed inventory rather than relying entirely on the departing person’s memory.
The engineering portion of an IT offboarding checklist should cover:
- Source control: organizations, repositories, teams, outside-collaborator access, forks, branch approvals, and code-owner assignments.
- Delivery systems: CI/CD, package registries, artifact stores, signing services, deployment environments, and release approvals.
- Runtime access: cloud roles, VPN or remote-access services, databases, production consoles, observability, and incident-management tools.
- Business continuity: domains, certificates, billing contacts, vendor support accounts, recovery contacts, and scheduled jobs.
- Information and equipment: documentation, issue trackers, approved local working copies, company devices, badges, and customer-provided assets.
For each entry, record the resource, identity or credential type, current owner, successor, required action, executor, deadline, and verification method. Keep secret values out of the ticket. Reference the approved vault or credential record instead.
Separate three questions that often get collapsed: Does the person have access? Do they own an asset or approval? Does a workload depend on something they created? Removing membership may answer the first question while leaving the other two unresolved.
For example, a departing engineer might no longer be able to log in, yet still be the only named reviewer on a protected deployment environment. The operational problem is an approval dependency, not necessarily a surviving credential. Fixing it requires an authorized replacement approver, not restoring the old login.
The inventory should also record uncertainty. If nobody knows who controls a registry account, mark it unresolved and assign an investigator. An empty cell must not be interpreted as “not applicable.”
3. Close human access beyond the primary login
Have administrators follow the actual identity architecture: disable or remove the appropriate account, remove relevant group assignments, address active sessions, and revoke application-specific access where necessary. Coordinate physical access and device handling through their owners. Do not assume every connected service implements the same deprovisioning behavior.
Microsoft’s access-revocation guidance explains an important limit: an application can maintain its own session token, and Microsoft Entra ID cannot directly revoke a token issued by that application. Your team needs to understand each critical application’s session controls and any interval before access is effectively removed.
Make the IT offboarding checklist distinguish “revocation requested,” “change applied,” and “effective access verified.” These states prevent a completed automation job from being mistaken for proof that every downstream session is closed.
Source-control removal also needs context. GitHub documents that former members may retain local repository copies, and some enterprise or fork arrangements can preserve access through other paths. Review the organization’s actual membership model and handle retained information through approved policies and agreements. Account removal is not remote erasure.
Use administrative evidence and approved validation methods; do not ask a colleague to impersonate the former engineer or request their personal passwords. Before deleting accounts or wiping devices, follow the organization’s retention and investigation requirements. Disabling access and destroying records are different decisions.
Cloud revocation deserves its own change review. AWS’s role-session revocation procedure can deny permissions to all older sessions for a role, not just one departing person. The administrator must select the mechanism appropriate to the identity setup and understand its scope. A broad emergency control can interrupt legitimate work if used indiscriminately.
For critical systems, require a second authorized reviewer to confirm the effective state and document known limitations. If a service cannot provide immediate session termination, record the exposure window, mitigation, accountable approver, and follow-up check. Do not silently label the system closed.
4. Move automation off personal credentials
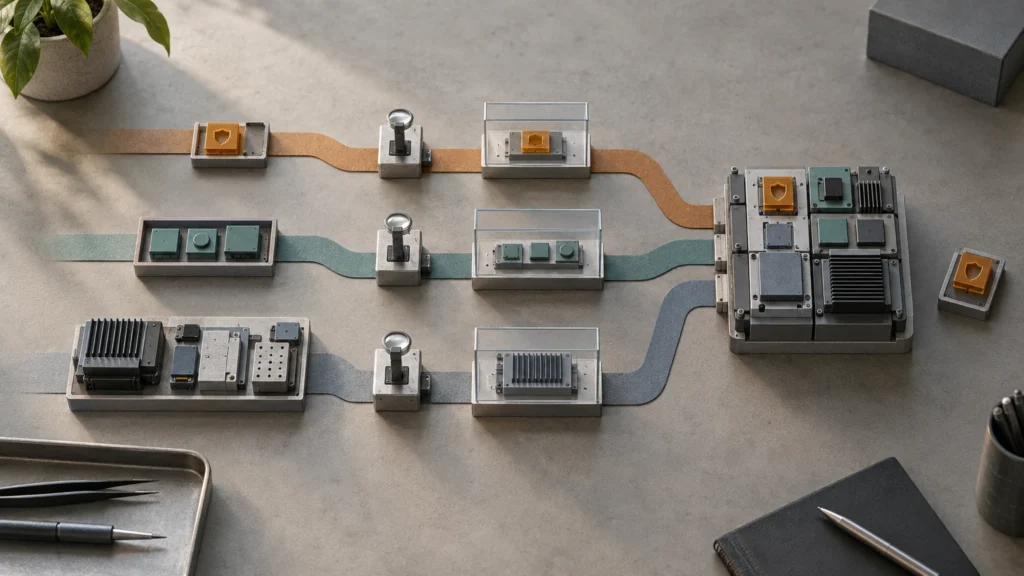
A release pipeline should not need a former employee’s identity to remain useful. Before a planned cutoff, identify jobs using personal access tokens, user-owned integrations, private SSH keys, individual cloud credentials, or recovery details that only one person controls. Review each dependency with the system owner.
Your IT offboarding checklist needs a workload-identity decision for each dependency: retire it, transfer its administration, or replace it with an approved organization-controlled mechanism. The right mechanism depends on the platform. A service account is not automatically safe simply because it lacks a person’s name.
Where a credential may have been copied or is no longer appropriately controlled, plan revocation or rotation. For a routine departure, sequence the work: establish an approved replacement, update authorized consumers, test the relevant job, revoke the old credential, and confirm the replacement still works. For suspected compromise, containment may require revocation first and a controlled service interruption.
GitHub’s deploy-key documentation illustrates why this review is separate from removing a user. A deploy key belongs to a repository rather than the person who created it and can remain active after that person is removed. Review who could possess the private key and which workloads depend on it; do not treat organization removal as sufficient evidence.
Do not bulk-delete machine credentials because their creator is leaving. Equally, do not preserve a former person’s interactive account indefinitely because a job still uses it. The accountable owner must decide how to remove the personal dependency while maintaining an approved operational path.
A hypothetical Friday exit
Consider an embedded backend engineer whose assignment ends Friday at 17:00 in the client’s agreed time zone. The inventory reveals a nightly package-publishing job using the engineer’s personal token, a repository deploy key, and a production approval rule naming that engineer.
The client’s platform owner replaces the publishing identity through the approved process and validates a controlled publish. The repository owner reviews the deploy key, replaces it where required, updates its authorized consumer, and revokes the previous key. The engineering manager assigns a qualified replacement approver. None of these actions requires sharing the departing engineer’s passwords.
At cutoff, administrators execute the human-access changes and collect evidence. Afterward, the successor verifies a build and a safe release path under the remaining team’s identities. The nightly job receives its own scheduled verification because a daytime build does not prove that it will run.
If that job cannot be verified until the following morning, the IT offboarding checklist records a pending continuity check, an owner, and a due time. It does not delay access revocation or pretend that the transition is fully verified. This distinction lets leadership see a manageable remaining task rather than a misleading all-green status.
5. Accept a demonstrated handover, not a document dump
Documentation is necessary, but the successor must be able to use it. Choose a small set of representative activities tied to the departing person’s responsibilities. The objective is evidence of operational readiness, not a requirement to transfer every fact the person has learned.
For a developer offboarding checklist, useful demonstrations can include:
- Building and testing a relevant service from the team’s documented setup.
- Preparing a change through review and the approved deployment path.
- Locating an alert’s owner, investigating it with authorized observability access, and identifying escalation options.
- Explaining the recovery procedure and exercising the safe portions in an appropriate environment.
- Finding open work, unresolved decisions, known failure modes, and the next owner for each.
A rehearsal must fit the risk. Do not trigger a production incident or perform a destructive restore merely to check a box. If an activity cannot be exercised safely, record the evidence available, what remains unproven, and the validation plan.
Make the successor the active operator during the handover, using their own authorized access. The departing engineer can explain or observe while still authorized. If the demonstration succeeds only because the departing engineer performs a hidden step, that step remains a transfer dependency.
Include the acceptance result in the IT offboarding checklist: activity, environment, operator, date, evidence, and remaining gap. “Runbook uploaded” is an artifact. “The successor followed the runbook and identified the recovery decision point” is evidence of understanding.
Reassign open pull requests, code ownership, deployment approvals, alerts, vendor conversations, and scheduled maintenance. Check whether the successor has both authority and available time. Assigning ten services to an already overloaded lead does not create ten services’ worth of operating capacity.
When a replacement is joining, connect the handover to a bounded onboarding plan. TechAID’s first-ten-days onboarding playbook provides a useful counterpart: build context, start with real limited-scope work, and expand ownership as readiness is demonstrated. An exit does not justify granting a new arrival every permission the predecessor accumulated.
6. Close with evidence and explicit exceptions
Keep access closure and delivery readiness as separate statuses in the IT offboarding checklist. A team can complete one while still working on the other. This prevents two dangerous shortcuts: leaving unnecessary access open to preserve delivery, or declaring the exit complete while nobody can support the service.
For each critical resource, retain a concise record of the authorized action, the responsible administrator, when it took effect, and how it was verified. Evidence might include an audit event, an administrative membership review, a completed credential change, or the successor’s controlled job execution. Store it where the appropriate reviewers can find it.
Use four clear outcomes:
- Verified: the required action and its intended result have been checked.
- Pending verification: the action is complete, but a scheduled or otherwise necessary check has not yet occurred.
- Approved exception: a named decision-maker has accepted a defined residual risk with mitigation, an expiry, and a review date.
- Unresolved: the owner, action, or effective state is still unknown and requires escalation.
An approved exception is not a permanent exemption. For example, a third-party application may need its vendor to complete an administrative transfer. Restrict what can be restricted now, assign someone to follow up, and document the missing confirmation. Do not keep an entire personal account active when only one narrowly defined administrative task is outstanding.
Your IT offboarding checklist should also distinguish access review from evidence preservation. Retain only the material your approved policy requires, limit who can view it, and avoid collecting unrelated personal information. The exit record should support an accountable decision, not become a copy of every conversation or file.
After cutoff, review relevant authentication and administrative events according to your security procedures. Unexpected activity requires investigation; absence of an alert alone is not proof of revocation. Recheck scheduled jobs, renewal contacts, and support ownership at their next relevant operating cycle.
The exit owner can then close the record with the appropriate technical and security reviewers. If anything remains open, the closeout must make that visible rather than hiding it behind a single completion percentage.
7. Agree the exit process before expanding a staffing engagement
An IT offboarding checklist is also a buyer-evaluation tool. Ask a potential staffing partner to walk through a planned roll-off and an immediate removal. You are testing coordination, clarity, and the boundaries of responsibility—not whether the partner promises that nobody will ever leave.
Contractor offboarding needs clear boundaries. In nearshore staff augmentation, the client should retain control of its identities, repositories, production permissions, and acceptance decisions. The provider can support agreed notifications, scheduling, transition coordination, and the assets it manages. The contract and operating procedure should make those boundaries explicit.
Ask these questions before access is granted:
- Who tells whom when an assignment changes, through which channel, and within what agreed interval?
- Who owns the access inventory, cutoff decision, and verification evidence?
- What handover work, overlap, availability, and commercial terms are agreed—and what happens if overlap is unavailable?
- Which devices, accounts, and records are client-managed versus provider-managed?
- How are an unverified removal, missing successor, or failed continuity test escalated?
Do not assume notification, replacement, or handover commitments that are absent from the agreement. Nearshore working-hour overlap can make live coordination easier, but it does not transfer administrative authority or eliminate the client’s management responsibilities.
TechAID’s partner-pilot framework can help make this discussion concrete. Include an exit-process walkthrough in the pilot’s operating review, alongside technical fit and communication. You do not need to terminate a real engagement to discover that neither side knows who controls a critical account.
The engagement model still matters. With direct hiring, your organization owns the permanent employment and operating arrangements. With project outsourcing, define delivery acceptance, access closure, and the ongoing support boundary for the workstream. Embedded augmentation does not become managed project delivery simply because a transition is difficult.
TechAID’s Verndale case describes a long-term staff-augmentation relationship involving QA leadership, knowledge sharing, and flexible capacity. The relevant lesson is operational integration: external professionals should strengthen a client’s ability to run its delivery system, not leave essential work dependent on one person.
Bring your current IT offboarding checklist and one role’s ownership map to a conversation with TechAID about nearshore staff augmentation. Ask how notification, transition coordination, and replacement onboarding would fit your existing management process. Keep the decision specific: what support is needed, what the client retains, and what evidence will confirm the transition worked.